All posts by Paul Raven

Machine-making machines making more machine-making machines…

RepRap 'Mendel' self-replicating machineVia Michael Anissimov we hear that the second generation of the RepRap self-replication machine, codenamed “Mendel”, is nearly ready for public release. Meaning that you could buy one (if you found someone who’d sell you one), but you could also build your own from the free open-source plans found at the RepRap website; the parts will cost you around US$650. [image from the RepRap wiki]

While such homebrew 3d printers aren’t currently much use for high-detail work and commercial finishes (like reproductions of your favourite World of Warcraft critters, maybe), they can make functional devices without any major problems. If there really is an increase in demand, you could probably assemble a Mendel and set it up to simple print a copy of itself. Then set up the copy to do the same, get a few generations of fully-functioning clones built, and then start churning ’em out and selling them to local buyers…

Integrating electrical and electronic circuits into physical parts is beyond these current home fabbers, but where big industry leads the homebrew crew will follow. Xerox has just invented a conductive silver ink that works without the need for a clean-room environment, meaning you can print off circuits onto a flexible substrate just like any other continuous-feed document. It wouldn’t take much for someone to buy some of that ink and find a way to use it in cheap and/or homebrew kit… hey presto, you’ve suddenly got the capability to replicate the electronic parts of a more complex self-replicating machine.

So go a bit further, integrate the two functions, have one machine that can print both inert blocks and electronics. Now we’re cooking! Now shrink ’em down, maybe speciate them so that different versions are specialised toward specific types of printing or assembly. But you’ll need to train them to pass off tasks they can’t do onto a machine that can, so you give them some sort of rudimentary swarm intelligence that communicates over something like Bluetooth… and then all of a sudden you’ve got an anthill of mechanical critters that have learned to procreate, cooperate, and deceive. DOOM.

Yeah, I know, it’s not very likely – but allow a guy a flight of robo-dystopian fancy on a Thursday, why don’t you? 🙂
Private security forces on the rise in Detroit

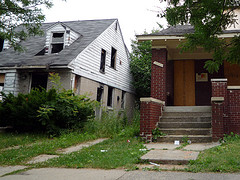
run-down Michigan real estateDetroit is arguably the reluctant poster-child for the bleeding edge of economic decline in the US, and as such it’s the place to watch to see how things might begin developing elsewhere. Which means that as the police – stretched by underfunding and escalating workload – concentrate their attentions elsewhere, we might start seeing an increase in private security firms patrolling some neighbourhoods. [via GlobalGuerillas; image by jessicareader]

Detroit’s problems come chiefly from its huge number of vacant foreclosed properties, which act as a magnet for criminality. The residents of those neighbourhoods who’ve managed to hold on to their homes (despite their plunge in value) are keen to see that their value doesn’t drop further, and so they’re willing to pay for surveillance and a visible presence – up to $30 per month, apparently.

But the line between surveillance and enforcement is a thin one, and as new security outfits proliferate, it’s not a stretch to imagine persons of less than scrupulous morals getting in on the only booming business in a broken town. And then it’s a short step to checkpoints at the barricades between neighbourhoods, armed patrols, CCTV saturation as only ever previously seen in the happy-go-lucky UK… sure, it’s a pessimistic scenario, but I wouldn’t say unrealistically so.

More likely is that the potential  threat of such an outcome will allow the gated community business model to proliferate. After all, property is cheap in the worst affected areas… so you go in, you by up a few streets, repair the broken buildings, install security infrastructure, and let out the properties with privacy and law enforcement served as a side-dish, paid for as part of the rent or mortgage payments. Hello, burbclaves.

What happens to the internet if there’s a viral pandemic?

Map of the internetOur beloved internet could suffer badly at the hands of a pandemic virus. And not just computer viruses, either: a pandemic attack of an illness like swine flu might have knock-on effects in the digital domain, and the US General Accountability Office isn’t pleased that no one appears to making any contingency plans [via SlashDot]:
… the Homeland Security Department accused the GAO of having unrealistic expectations of how the Internet could be managed if millions began to telework from home at the same time as bored or sick schoolchildren were playing online, sucking up valuable bandwidth.

Experts have for years pointed to the potential problem of Internet access during a severe pandemic, which would be a unique kind of emergency. It would be global, affecting many areas at once, and would last for weeks or months, unlike a disaster such as a hurricane or earthquake.

H1N1 swine flu has been declared a pandemic but is considered a moderate one. Health experts say a worse one — or a worsening of this one — could result in 40 percent absentee rates at work and school at any given time and closed offices, transportation links and other gathering places.

And what do you do if you’re stuck home from work or school under house quarantine? You fire up your computer and mess around on the internet (unless that’s just me), meaning a severe pandemic will cause a serious uptick in bandwidth demand, potentially slowing down essential infrastructure systems at the same time. [image by matthewjethall]

In a rare display of pragmatism, Homeland Security has told the GAO that there’s not really much it can do to prepare for this sort of eventuality – despite theories to the contrary, the internet is not a series of tubes. Commercial ISPs are unlikely to be keen on being told to lock down the connections of their customers, either.

Homeland Security might well have spent a moment to think about the psyops angle of such a move, as even the positive practical results of restricting consumer bandwidth might be seriously outweighed by the psychological negatives. Ill internet habitués might break quarantine to go to locations where the connection was faster; the state of fear and paranoia that attends a serious pandemic might be amplified by the perceived restriction of information channels (“what are they trying to hide?”)… having technological impossibility as a scapegoat is probably something of a relief.

The good news, however, is that most of the major securities exchanges and financial institutions have their own private networks that don’t rely on publicly-available bandwidth, so we can rest easy in the knowledge that, even when we’re stuck at home sweating out a nasty virus without so much as a bit-rate that’ll let us peer at Fark every ten minutes, greedy shysters in expensive suits will still be able to skim the cream from the global misery without any inconvenience.

Frankly, I’m not sure that the issues would be as big as is being suggested; schools and businesses surely contribute significantly toward bandwidth consumption during the daytime, so there’d be some slack to take up thanks to absenteeism. The whole thing has a slight smell of Millennium Bug about it, at least for me; if there’s a networking expert in the audience, I’d appreciate being set straight on the details.

And while we’re talking about the internet, good old DARPA – who invented the thing in the first place – are trying to work out how to extend it into orbit and link up our swarm of satellites to their own broadband connections. That’s easy enough (though still slow) when you can set up a persistent link from ground to orbit with a geostationary platform, but not so simple for sats that move relative to the Earth’s surface. If you’ve got an idea of how to get around the problem, DARPA would like to hear from you before 5th November…

… but in the meantime, would anyone like to open a book on how soon a military or commercial satellite will be hacked over its own broadband connection?

The Facebook graveyard

metaverse tombstoneThis week’s big social network story is Facebook’s announcement that they now allow the user profiles of people who’ve died to be “memorialised” – frozen in perpetuity (one presumes) so that you can still visit them, like some digital tombstone or memorial bench. [image by moggs oceanlane]

As that blog post makes clear, Facebook are obviously reacting to a genuine human need, though it would be easy (if highly cynical) to suggest that they’d like a slice of the growing traffic for online memorial sites, as mentioned earlier this month. But questions remain – who will maintain these profiles, and for how long? Will they drop out of the system when their last friend connection is severed (assuming, of course, that any social network platform lasts long enough for that to happen)? Will those memorial profiles be any more or less transferrable to new networks than those of the living? Will the memorials still have adverts surrounding them, like a normal Facebook page, and is that a morally acceptable price for their maintenance?

The biggest question is obviously “how much checking will Facebook do to ensure that the person really is dead?” Internet “pseuicides” aren’t a new phenomenon, and it’s not clear whether the Facebook crew have a procedure in mind to prevent a group of friends faking a death, be it in collusion with the owner of the profile in question or otherwise. Given how easy it is to hack many people’s public email accounts (poor password choices, easily reverse-engineered ‘secret questions’, etc.), unless they demand some sort of legal confirmation from the state that the owner has indeed passed away it could be a relatively simple scam to declare a living person to be deceased. Indeed, that might even become a popular black economy service, alongside fake IDs and new identities.

Head-mounted augmented reality computers: the budget hack versus the bespoke device

One of the more interesting things about the hardware hacking scene is comparing the results of different methodologies. Some folk prefer to develop gadgets that are as close to production-grade products as possible, while others are more focussed on the low-budget proof-of-concept kludge… and this week has seen examples of both approaches as applied to augmented reality visor-computers.

First up, the craftsman approach. Pascal Brisset was frustrated with wearable computer cooncepts that relied on some sort of back- or belt-mounted processor unit to drive the headset, so he decided to build the whole system onto an off-the-shelf visor VDU [via Hack A Day]. As you can see, the results are pretty compact:

Pascal Brisset's wxhmd wearable computer

It runs on Linux, too, but that probably went without saying. Of course, it’s just a proof-of-concept rather than something that Brisset could start building for consumers. As he states in his documentation disclaimers:

The systems draws 1 A with no power optimizations. This is acceptable since nobody would want to spend more than a few minutes with two pulsed microwave RF transmitters, an overheating lithium battery and eye-straining optics strapped to their forehead anyway.

Quite.

Meanwhile, down at the other end of the brain-farm, Andrew Lim built himself a backyard VR helmet using nothing more than an HTC Magic handset and a few dollars worth of other gubbins [also via Hack A Day]. It’s quite obviously a much more lo-fi affair than Brisset’s contraption:

It does have a certain goofy charm, doesn’t it? But again, hardly the sort of thing you’d try selling for any practical purpose whatsoever – the point being proven here is that augmented reality (and other similar emerging technologies) are not necessarily the exclusive domain of big corporations or slick new start-ups; where there’s a will (and some ingenuity), there’s a way. Or, as I often end up saying here, Everything Can (And Will) Be Hacked.

Personally, I find that reassuring, because the battle for direct access to our retinas is just starting to heat up. The big tech corporations can see there’s money to be made with wearable tech in the very near future, and they’re preparing to roll out the hardware as soon as next year (if press releases are to be trusted, which they quite possibly aren’t)… and as Jan Chipchase pointed out, the way they’ll make the stuff affordable to you is by co-opting with companies who’re desperate for the direct pipeline to your brainmeat that said hardware will provide. They need to ride that augmented reality hype curve, after all – at least until it reaches the trough of disillusionment.